Shows

Practical DevSecOpsBest Black Friday Cybersecurity Certification Deals (2026) – AI Security SavingsAre you looking to maximise your Q4 training budget and advance your career in cloud-native security, DevSecOps, or AI security? In this special episode, we break down the Practical DevSecOps Black Friday 2026 sale, covering exclusive discounts across 11 professional certifications and 14 target course bundles.Discover how to save 15% on individual credentials and up to $697.90 on multi-certification packages. We examine why over 12,500 security professionals and major enterprises such as Accenture, Booz Allen Hamilton, IBM, PwC, and PayPal trust these lab-driven, task-based certifications.https://www.practical-devsecops.com/black-friday-sale-2026/
2026-11-1718 min
Practical DevSecOpsAI Cybersecurity InfoSec Deals - Black Friday Sale 2026Practical DevSecOps is offering 15% off all single certifications and total bundle discounts of up to $600 during this Black Friday CyberMonday Sale 2026.Pricing Page:https://www.practical-devsecops.com/pricing/Featured Certification Bundles:DevSecOps & AI Security (CDP + CAISP): Combines secure SDLC fundamentals with AI threat modeling and LLM security for $1,619.10 (saving $478.90).Full AI & Agentic Security Track (CAISP + CMCPSE + CAASE): Covers AI model security, Model Context Protocol (MCP) server security, and agentic AI defenses for $2,186.10 (saving $610.90).Infrastructure & A...
2026-11-0619 min
Practical DevSecOpsThe Rise of Forward Deployed AI Engineers in 2027Why is the Cybersecurity AI Forward Deployed Engineer emerging as one of tech’s most critical roles, commanding compensation of up to $235,100? In this episode, we explore why agentic security has reached an urgent turning point, with 88% of organisations confirming or suspecting an AI agent security incident in the past 12 months. As enterprises rapidly grant autonomous agents live credentials and production database access, market demand for forward-deployed talent has surged by 1,165% year-over-year.Certified Agentic AI Security Expert Course:https://www.practical-devsecops.com/cert...
2026-10-0822 min
Practical DevSecOpsGuarding the AI Software Supply Chain - Product Security Roles Report 2026we explore key insights from the State of Product Security Roles: 2026 Research Report. As AI-generated code and autonomous AI agents transform software production, product security is shifting from narrow application scanning to full lifecycle protection. We break down how top organizations are navigating severe talent shortages, structuring modern security teams, and securing the AI supply chain.What You’ll Learn in This Episode:The 2026 Skills Shortage: Why 59% of security leaders report a critical or significant skills gap in cloud-native and AI/LLM security, and how...
2026-09-3022 min
Practical DevSecOpsTop AI Certifications for 2026: CAISP vs SecAI+ vs AAISCertified AI Security Professional (CAISP), CompTIA SecAI+, and ISACA AAISM represent the premier credentials competing for cybersecurity professionals in 2026 as demand for AI security roles surges. In this episode, we break down how these certifications stack up for engineers looking to defend real-world production stacks against novel AI vulnerabilities. With job postings requiring AI security skills doubling and red-teaming roles projected to grow by 35%, choosing the right certification pathway has never been more critical for your career trajectory.CAISP, SecAI+, and Microsoft Azure AI Security highlight the fundamental shift b...
2026-09-1408 min
Practical DevSecOpsAI Security Skills: What to Learn in 2027 | AI Cybersecurity Certification TrainingReady to secure your career in 2027? Enroll in the Certified AI Security Professional (CAISP) course today. This vendor-neutral, fully lab-based certification from Practical DevSecOps is trusted by global organizations like IBM, Accenture, and PwC. It offers over 30 browser-based labs and a rigorous six-hour practical exam to prove you can actively secure real AI architectures.In this episode of the podcast, we dive into the exact skills you need to stay ahead of the curve as AI-driven systems take over production environments. We discuss:The Salary Premium: Why AI security...
2026-09-0421 min
Practical DevSecOpsBattle of the AI Red Team Certifications: CAISP vs. OSAI vs. SANS SEC536In this episode, we dive deep into the field of AI security to compare the top three AI red teaming certifications of 2026: Practical DevSecOps' Certified AI Security Professional (CAISP), OffSec's AI Red Teamer (OSAI/AI-300), and SANS's SEC536 (Adversarial AI). Whether you are an experienced pentester or an AppSec engineer looking to pivot into securing LLMs, we break down exactly what you get for your money, contrast the intensity of their practical labs against their exam formats, and analyze which credential offers the strongest career and salary growth potential.
2026-08-1405 min
Practical DevSecOpsBest Application Security Courses Compared 2026 - AppSec TrainingsIn this episode, we break down the 2026 application security space to help you decide which training path actually moves the needle for your career. The central theme of our discussion is a critical choice every professional faces: are you looking to build hands-on skills you can use on Monday morning, or are you looking for a credential to bolster your resume?We explore the certifications that hiring managers and AppSec leads are prioritizing this year, with a heavy focus on practical, lab-based learning over traditional multiple-choice exams.
2026-07-1421 min
Tech Jobber PodcastBreaking Into DevSecOps: The Career Path Nobody Talks AboutDevSecOps is one of the highest-paying non-coding tech careers in 2026 — with senior DevSecOps and DevOps roles paying $250K–$300K+ as individual contributors.
In this episode, global DevSecOps leader Ratzil Rodriguez breaks down the DevSecOps career path, how DevOps vs DevSecOps actually differ, cloud security, large-scale cloud migration, and the exact skills you need to become a DevSecOps engineer without a traditional coding background.We unpack how to break into DevSecOps from network admin, cybersecurity, or platform engineering — and why "shifting left" on security is the skill companies are desperate to hire for. Ratziel shares what he look...
2026-06-2933 min
Practical DevSecOpsElite Pay for MCP Security Experts: Mastering the AI Integration LayerAs organizations rapidly adopt the Model Context Protocol (MCP) to connect AI agents to production data and internal tools, a massive security gap has emerged. In this episode, we explore why MCP security has become one of the fastest-rising hiring signals in the cybersecurity industry and how mastering these skills can dramatically increase your salary potential.Featured Resource: Learn more about the Certified MCP Security Expert (CMCPSE) course by Practical DevSecOps, focusing on attacking, assessing, and hardening MCP servers through browser-based labs.In this e...
2026-06-2922 min
Practical DevSecOpsMCP Security Best Practices 2026 - Certified MCP Security Expert Course (CMCPSE)The high-speed adoption of AI agents has a new "default" language: The Model Context Protocol (MCP). While MCP provides a seamless way for Large Language Models (LLMs) to interact with tools, databases, and APIs, it has also introduced significant new attack surfaces. In this episode, we break down the MCP Security Best Practices: 2026 Playbook to help security engineers and developers move beyond theory and into hardened, production-ready defense.What’s at Stake?Recent research has exposed a "wild west" of MCP implementations. Security scans of nearly 2,000 publicly acc...
2026-06-0520 min
Practical DevSecOpsBuilding a Resilient MCP Security Program for Security ProfessionalsIn this episode, we dive into the "MCP Security Risk Framework for Enterprise CISOs", exploring how to secure AI agents against the unique threat of agentic amplification. Ready to lead your organisation’s AI security strategy? Upskill your team with the Certified MCP Security Expert (CMCPSE) course, featuring over 30 hands-on labs to attack, defend, and pen test MCP serversUnlike standard API risks, which are bounded to specific data or functions, MCP risks are non-linear because a single compromised connection can cascade across every capability an agent holds. This "capability multiplier" effe...
2026-05-2621 min
Practical DevSecOpsOWASP MCP Top 10: 2026 Security Framework and MCP Security CertificationIn this episode, we dive deep into the OWASP MCP Top 10, the first official security framework dedicated to the Model Context Protocol (MCP). Ready to lead your team’s AI security strategy and bridge the skills gap?Enroll in the Certified MCP Security Expert (CMCPSE) Course today!Get hands-on experience in tool poisoning labs, OAuth 2.1 hardening, MCP red-teaming, and shadow server detection. This is the definitive certification to secure agentic AI in 2026.This framework addresses a critical shi...
2026-05-0620 min
Practical DevSecOpsNavigating the Path to Application Security Manager in 2026Transitioning from a technical engineer to an Application Security (AppSec) Manager is rarely a straight line; it requires balancing technical expertise with the strategic mindset needed to lead a department. In this episode, we break down the realistic 5–8 year career path for aspiring leaders, moving from hands-on development to managing end-to-end security programs. We dive into the "messy reality" of the role, where you must act as the bridge between fast-moving engineering teams and CTOs focused on the bottom line.Learn why the Security Champion phase is the most cri...
2026-04-2421 min
Practical DevSecOpsDevSecOps Certification Guide: CDP vs. ECDE Comparison and CoursesWelcome to The DevSecOps Edge, the podcast dedicated to helping you become one of the top 1% of cybersecurity engineers in the industry. In a world where APIs account for 80% of internet traffic and 94% of web breaches start at the API layer, staying ahead of the curve isn't just an advantage—it's a necessity.In our featured episodes, we tackle the biggest questions facing security professionals today. Our deep-dive comparison, "CDP vs. ECDE: Which DevSecOps Certification Is Worth Your Time?", breaks down the critical differences between the Certified DevSecOps Professional (CDP) and EC...
2026-04-0319 min
The ITSM Practice: Elevating ITSM and IT Security KnowledgeDevSecOps: Responsibility Without AuthorityDevSecOps promises shared security responsibility, but what happens when accountability shifts without decision authority? In this episode of The ITSM Practice Podcast, Luigi Ferri explores governance gaps, risk ownership, Security Champions, burnout, and structural ambiguity in DevSecOps. A sharp reflection for CISOs, AppSec leaders, and ITSM professionals navigating security governance and enterprise risk management.In this episode, we answer to:Who is explicitly allowed to accept risk in a DevSecOps operating model?What happens when developers receive security accountability without authority?Are Security Champions strengthening governance, or masking...
2026-03-3106 min
Practical DevSecOpsExploiting Hidden Endpoints and Centralizing Defense with Kong - Your API Documentation is a LieIs your API documentation telling the truth? In this episode, we dive into the uncomfortable reality that API documentation is often a "lie" because of the gap between Swagger files and what is actually running in production. We explore how attackers exploit this gap using advanced fuzzing techniques and JWT manipulation, and why a centralised defense strategy using Kong API Gateway is the only way to effectively secure modern microservices.Key Topics Covered:The JWT Illusion: We debunk the myth that JSON Web Tokens (JWTs) are inherently...
2026-03-2020 min
Practical DevSecOpsCAISP vs. OSAI Certification Comparison Guiden this episode, we tackle the rapidly evolving landscape of artificial intelligence and the critical need for specialized security expertise. As Large Language Models (LLMs) and autonomous agents become integrated into the modern enterprise, they bring a new set of risks, including prompt injection, training data poisoning, and insecure plugin designs. To help you navigate your career path in this high-demand field, we provide an in-depth comparison of two premier certifications: the Certified AI Security Professional (CAISP) from Practical DevSecOps and the Advanced AI Red Teaming (OSAI) from OffSec.What Yo...
2026-03-0522 min
Mission Critical: Defense RecruitingDevSecOps in Practice Across Defense and National Security | Yolanda ClarkeDevSecOps is talked about constantly in defense and national security. Very few leaders actually have to make it work in real mission environments. In this episode of Mission Critical: Defense and Aerospace Recruiting, Katherine Jerald sits down with Yolanda Clarke, Founder and CEO of Powder River Industries, to break down what DevSecOps looks like when failure is not an option. Yolanda explains how DevSecOps must be designed into programs from day one, not bolted on at the end, and why treating security as a core design requirement is the only way to deliver speed...
2026-03-0434 min
Practical DevSecOpsSLSA Framework: The Definitive Guide for Securing Your Software Supply ChainIn this episode, we dive deep into the SLSA (Supply-chain Levels for Software Artifacts) framework, the definitive standard for securing your software supply chain. With software supply chain attacks increasing by 742% between 2019 and 2022, understanding frameworks like SLSA—pronounced "salsa"—is no longer optional; it is an operational reality.We explore the origins of SLSA, which began at Google as "Binary Authorization for Borg" before being contributed to the Open Source Security Foundation (OpenSSF) in 2021. We break down what SLSA provides: a common vocabulary for security maturity, verifiable provenance metadata, and incremental security levels that...
2026-02-2822 min
VIA Knowledge Hub PodcastHow to break into DevSecOps (without expensive bootcamps) with Damien BurksDevSecOps is everywhere right now, but most teams are still treating it like a tooling problem. Damien Burks says it's actually a culture problem. He's a DevSecOps expert and the founder of the DevSec Blueprint, a free, open-source learning guide with a 650+ member community. His mission: help people break into DevSecOps by focusing on foundations and systems thinking, not expensive bootcamps.In this episode, Damien explains why DevSecOps engineers are “the glue”, the people connecting developers, operations, legal, and compliance into a single security-minded team. He walks through the patterns that repeat across every cloud platform, why the...
2026-02-2639 min
Practical DevSecOpsDevSecOps Statistics in 2026: Market Growth, Adoption Trends, and Strategic InsightsIn this episode, we explore the explosive growth of the DevSecOps market, which is projected to reach between USD 8.58 billion and USD 10.88 billion by 2026. Driven by cloud-native transitions, AI integration, and intensifying regulatory pressures, the industry is witnessing a compound annual growth rate (CAGR) of up to 22.10%.Course Page: https://www.practical-devsecops.com/certified-devsecops-professional/What You’ll Learn in This Episode:• The Financial Landscape: Why DevSecOps engineering has become a high-demand career with massive salary potential. We break down the 2026 salary bench...
2026-02-2015 min
Practical DevSecOpsLLM Jacking – The $46,000-a-Day Security ThreatIn this episode, we dive deep into one of the most pressing financial and security threats facing organizations in 2026:Featured Resource: If you are responsible for securing AI infrastructure, this episode highlights the technical controls covered in the Certified AI Security Professional (CAISP) course, which includes hands-on labs for defending against the OWASP Top 10 LLM vulnerabilities and mastering the MITRE ATLAS framework.LLM Jacking. While many security discussions focus on prompt injection or model poisoning, LLM jacking is a different beast entirely—it is a direct infrastructure compromise...
2026-02-0913 min
Practical DevSecOpsBreaking the Cycle: From Red Teaming to DevSecOps LeadershipIn this episode, we explore the remarkable career transformation of Hiroshi Tanaka, a security veteran with 15 years of experience in offensive security, penetration testing, and red team operations. Despite his extensive background in a Fortune 500 company, Hiroshi realised that his ability to "break things" was no longer sufficient as his organisation transitioned towards DevOps and cloud-native development.He shares his candid journey of overcoming the fear of becoming "irrelevant" and the challenge of preventing vulnerabilities during development rather than just finding them in production. We dive deep into the s...
2026-01-2214 min
Practical DevSecOpsAgentic AI Security Threats, Defenses, Evaluation & Open ChallengesAI Security Certification and Training:https://www.practical-devsecops.com/certified-ai-security-professional/To address these challenges, the Certified AI Security Professional (CAISP) certification provides the skills needed to secure the AI supply chain and infrastructure. The course covers:The emergence of Agentic AI represents a fundamental paradigm shift in cybersecurity. Unlike traditional, static software, agentic systems are defined by their autonomy, planning capabilities, and ability to use tools to execute multi-step goals. This shift means defenders are no longer just securing code, but rather dynamic, goal-driven...
2026-01-1312 min
Practical DevSecOpsNavigating the DSOMM Roadmap and the DevSecOps RevolutionThis episode focuses on how these principles fit into the DevSecOps Maturity Model (DSOMM), a structured framework that enables organisations to embed security practices from the start, ensuring that rapid delivery does not come at the cost of protection.Ready to take the first step?The Certified DevSecOps Professional (CDP) course is the ultimate starting point for those looking to automate security and lead organisational change. Through 100+ hands-on labs, the CDP program teaches you to build secure CI/CD pipelines using SCA, SAST, a...
2026-01-0617 min
Practical DevSecOpsTop 10 Emerging AI Security Roles in 2026Secure your future in the most critical career path in tech by enrolling in the Certified AI Security Professional (CAISP) course today!In this episode, we explore the definitive guide to the Top 10 Emerging AI Security Roles for 2026. The shift toward AI-integrated operations is not a future concern—it is happening now, and it has opened a "chasm" in the workforce that only specialised professionals can fill. We break down the responsibilities, required skills, and massive salary potential for the roles that will define the next decade of cybersecurity.K...
2025-12-2415 min
Practical DevSecOpsAI Security Interview Questions - AI Security Training and Certification - 2026Enroll now in the Certified AI Security Professional (CAISP) course by Practical DevSecOps! This highly recommended certification is designed for the engineers , focusing intensely on the hands-on skills required to neutralize AI threats before attackers strike. The CAISP curriculum moves beyond theoretical knowledge, teaching you how to secure AI systems using the OWASP LLM Top 10 and implement defenses based on the MITRE ATLAS framework. You will explore AI supply chain risks and best practices for securing data pipelines and infrastructure. Furthermore, the course gives you hands-on experience to attack and defend La...
2025-12-1716 min
Practical DevSecOpsBest AI Security Certification Courses & Earn $280K Salary Premium in 2026The cybersecurity market is currently experiencing a massive talent shortfall in the emerging field of Artificial Intelligence security, driving compensation for specialized roles to unprecedented heights. AI security roles are projected to pay between 180K–280K in 2026, but the majority of cybersecurity professionals lack the necessary qualifications,. We break down exactly what skills are commanding this premium and how to close the gap.Organizations are urgently seeking experts who can secure LLM deployments, stop prompt injection attacks, and lock down complex AI pipelines. Generalist security cert...
2025-12-1114 min
Practical DevSecOpsBecome an AI Security Engineer in 8 Weeks - Fast-Track Guide & RoadmapCybercrime drains trillions of dollars globally each year. Today's threat landscape is defined by smart, adaptable adversaries: 40% of all cyberattacks use AI to find hidden weaknesses, and nearly all companies (93%) now face these advanced threats daily. The Certified AI Security Professional (CAISP) course compresses the typical 2–4 years needed to become an AI Security Engineer into just 8 weeks through daily hands-on labs with vulnerable AI systems. This episode describes the roadmap for defending against sophisticated AI threats, drawing from the AI Security Engineer Roadmap: Skills for 2025 & Beyond.AI security engineers are...
2025-12-0313 min
Practical DevSecOpsAI Security Certification: The Ultimate Guide to the Certified AI Security Professional (CAISP) courseEpisode: Securing AI Systems - A Deep Dive into AI Security with Marudhamaran Gunashekaran In this episode, Jeremy Daly, Cybersecurity Lead at Lumifi, sits down with Marudhamaran Gunashekaran, Principal Security Consultant and Lead Author of the Certified AI Security Professional (CAISP) course at Practical DevSecOps (a Hysn Technologies company). What You'll Learn: The conversation cuts through the AI security hype to address what matters. Maran identifies the biggest threat facing organizations today: rapid, uncontrolled AI adoption. Companies are rushing to i...
2025-11-2450 min
Practical DevSecOpsInfoSec Black Friday Certification Deals 2025InfoSec Black Friday Deals 2025: Securing the Future of CybersecurityThis special offer broadcast details the InfoSec Black Friday 2025 deals, presenting a limited-time chance to advance cybersecurity careers when the demand for security professionals continues to grow. Tune in to discover how to save up to $500 on certification bundles and receive 15% off all individual certifications. Certified DevSecOps Professional (CDP)Certified AI Security Professional (CAISP)Certified Cloud-Native Security Expert (CCNSE)Certified Threat Modeling Professional (CTMP)...
2025-11-1311 min
InfosecTrainDevSecOps in the Age of AI and Automation | Secure DevOps ExplainedThe world of DevSecOps is changing rapidly with AI and automation. In this session, we explore how intelligent security practices are transforming development pipelines, making them smarter, faster, and more secure for modern organizations.📘 What You’ll Learn:DevSecOps in 2025+ and why it mattersTransitioning from traditional to intelligent DevSecOpsAI and automation trends shaping secure DevOps workflowsVision 2030: strategies to future-proof DevSecOpsReal-world examples of DevSecOps in actionThis episode is essential for D...
2025-09-2823 min
Practical DevSecOpsHow Security Consultant Can Transition to AI Security Engineer in 2025In this episode, we explore the rapid evolution of cybersecurity and the critical rise of a new specialisation: the AI Security Engineer. As artificial intelligence advances, it not only enhances our defensive capabilities but also introduces sophisticated new attack vectors that traditional security measures can't handle.AI Security Certification - Certified AI Security Professional (CAISP) courseThis has created a massive demand for professionals who can secure the AI systems themselves, with an estimated 4.8 million unfilled cybersecurity positions worldwide and a significant shortage of experts skilled in both AI and cybersecurity....
2025-09-1821 min
Practical DevSecOpsAI Red Teaming Guide for Beginners in 2025This episode delves into the critical field of AI Red Teaming, a structured, adversarial process designed to identify vulnerabilities and weaknesses in AI systems before malicious actors can exploit them.The Certified AI Security Professional (CAISP) course is specifically designed to advance careers in this field, offering practical skills in executing attacks using MITRE ATLAS and OWASP Top 10, implementing enterprise AI security, threat modelling with STRIDE, and protecting AI development pipelines. This certification is industry-recognized and boosts an AI security career, with roles like AI Security Consultant...
2025-09-0820 min
Practical DevSecOpsFrom DevSecOps to AI Security: 6,429 Pros Trained. - Here’s the DataSecurity isn't keeping pace with the swift advancements in AI and the explosion of cloud-native adoption. Many teams find themselves trying to mend broken pipelines with outdated AppSec playbooks, leading to significant vulnerabilities. This episode dives deep into how to bridge this critical gap, equipping you with the skills to truly defend modern systems.Ready to build these skills and stay ahead of the curve?Enroll in the Certified DevSecOps Professional and Certified AI Security Professional (CDP + CAISP) bundle today and save! P...
2025-07-3012 min
InfosecTrainDevSecOps in 2025: Top Trends, Tools & Future-Proof StrategiesCurious about how DevSecOps is transforming in 2025? This episode explores the future of secure development, spotlighting the trends, tools, and innovations that are redefining how teams build and protect software.From AI-powered security automation to the rise of Zero Trust pipelines, we cover the must-know shifts shaping modern DevSecOps. Whether you're a developer, security engineer, or tech leader, this session offers future-ready insights and actionable takeaways to strengthen your DevSecOps strategy.📘 What You’ll Learn:➡️Key DevSecOps trends shaping 2025➡️Security automation & AI-driven tools➡️Integration of Zero Trust in CI/CD pipelines➡️Compliance...
2025-07-2126 min
Practical DevSecOpsBest AI Security Books in 2025Are you ready to face the escalating threat of AI attacks? AI system attacks are hitting companies every single day. Hackers use AI tools to break into major banks and steal millions. It's a critical time for anyone in tech or cybersecurity to understand how to fight back.In this episode, we delve into why AI security is more crucial than ever in 2025. We reveal that 74% of IT security professionals say AI-powered threats are seriously hurting their companies, and a staggering 93% of businesses expect to face AI attacks daily this year.These aren't just minor i...
2025-06-2012 min
The Security RepoAI, Zero Trust, And The Future Of DevSecOps In A Cloud-First World – Nivathan Athiganoor SomasundharamIn this episode of the Security Repo Podcast, we dive deep into the evolving role of DevSecOps with Nivathan Athiganoor Somasundharam, a technical account manager at Teleport. He shares his journey from cloud engineering to becoming a DevSecOps practitioner, emphasizing proactive security, the elimination of secrets, and the future of identity-based infrastructure access. We also explore how AI can enhance DevSecOps practices and the cultural shift needed to embed security across development and operations.https://www.linkedin.com/in/nivathan/https://goteleport.com/Nivathan Athiganoor Somasundharam is a technical account manager at Gravitational Inc. DBA Teleport. He specializes in...
2025-06-1819 min
Practical DevSecOpsThreat Modeling for Medtech IndustryJoin us for an insightful episode as we delve into the critical realm of product security within the Medtech industry. The digital revolution is transforming patient care, but it also introduces significant security risks to medical devices.We'll explore the complex security environment where devices like pacemakers and diagnostic systems are increasingly connected, making them targets for unauthorised access, data theft, and operational manipulation. Discover how breaches can lead to dire consequences, from endangering patient health and damaging manufacturers' reputations, to incurring financial losses and n...
2025-06-1805 min
Practical DevSecOpsAI Security Frameworks for EnterprisesWelcome to "Securing the Future," the podcast dedicated to navigating the complex world of AI security. In this episode, we unpack the vital role of AI security frameworks—acting as instruction manuals—in safeguarding AI systems for multinational corporations. These frameworks provide uniform guidelines for implementing security measures across diverse nations with varying legal requirements, from Asia-Pacific to Europe and North America.We explore how these blueprints help organizations find weak spots before bad actors do, establish consistent rules, meet laws and regulations, and ultimately build trust with AI users. Crucially, they enable compliance and r...
2025-06-1205 min
Practical DevSecOpsGlobal Banks Slash Security Costs 5X with Threat Model TrainingDiscover how a global financial institution transformed its security posture and achieved massive cost savings through targeted threat modeling training. Facing challenges like inconsistent practices, difficulty scaling training across 50 countries, and keeping pace with evolving threats, this bank needed a new approach beyond infrequent, in-person workshops.Their solution? Leveraging the Certified Threat Modeling Professional (CTMP) course from Practical DevSecOps. This program offered a practical learning approach with extensive hands-on labs simulating real banking scenarios and crucial 24/7 expert support via Mattermost. It covered key methodologies like STRIDE an...
2025-06-0211 min
TechDaily.aiDevSecOps Maturity Model: A Roadmap to Secure, Scalable Software DeliveryStruggling to make DevSecOps work in your organization, even though everyone agrees it's crucial? You're not alone—and this episode is here to help. Join us as we break down the DevSecOps Maturity Model, a powerful framework to assess your current capabilities, define where you want to go, and create a step-by-step path to get there.In this episode, you’ll learn:The 4 stages of DevSecOps maturity: Beginner, Intermediate, Advanced, and ExpertThe 6 key competencies: from people & culture to observability & incident responseHow to conduct a DevSecOps self-assessment and map your improvement journeyWhy “baking in” security (not bolting it on) i...
2025-05-0715 min
Podd om digitalisering - EffektenBygg säkra applikationer: Guide till DevSecOps. Erik Hjalmarsson (# 226)
Att integrera säkerhet i utvecklingsprocessen genom DevSecOps, med fokus på utbildning, verktyg för sårbarhetsanalys, och förbättrat samarbete mellan säkerhets- och utvecklingsteam.
Erik Hjalmarsson, Cloud Architect på Sogeti, med en introduktion till DevSecOps från utvecklingsperspektivet. DevSecOps handlar om att integrera säkerhetsarbetet i den dagliga utvecklingsprocessen. Det innebär ett samarbete och delat ansvar mellan säkerhetsteamet och utvecklingsteamen. Historiskt har det funnits en obalans där ett litet säkerhetsteam har haft ansvaret för alla säkerhetsaspekter, vilket har varit svårt att hantera. Genom DevSecOps kan säkerhetsarbetet bli en naturlig de...
2024-11-2420 minEffekten | digitalisering - kunskapBygg säkra applikationer: Guide till DevSecOps. Erik Hjalmarsson (# 226)Att integrera säkerhet i utvecklingsprocessen genom DevSecOps, med fokus på utbildning, verktyg för sårbarhetsanalys, och förbättrat samarbete mellan säkerhets- och utvecklingsteam.
Erik Hjalmarsson, Cloud Architect på Sogeti, med en introduktion till DevSecOps från utvecklingsperspektivet. DevSecOps handlar om att integrera säkerhetsarbetet i den dagliga utvecklingsprocessen. Det innebär ett samarbete och delat ansvar mellan säkerhetsteamet och utvecklingsteamen. Historiskt har det funnits en obalans där ett litet säkerhetsteam har haft ansvaret för alla säkerhetsaspekter, vilket har varit svårt att hantera. Genom DevSecOps kan säkerhetsarbetet bli en naturlig del i alla utveckl...
2024-11-2420 min
The Application Security PodcastKayra Otaner -- DevSecOpsKayra Otaner joins the podcast today to discuss DevSecOps and answer the question, is it dead? Kayra is the Director of DevSecOps at Roche and is highly involved in the DevSecOps community. Kayra states that DevSecOps in its traditional form is “dead” and that each organization should approach its needs based on their size. Otaner introduces the concept of "security as code" and "policy as code" as more effective approaches, where security functions are codified rather than relying on traditional documentation and checklists. Finally, they discuss the emergence of Application Security Posture Management (ASPM) tools as the "SIM for AppS...
2024-10-2932 minThe ITSM Practice: Elevating ITSM and IT Security KnowledgeIntegrating Security and Service: The Convergence of DevSecOps and ITIL® 4Welcome back! In today's episode of "The ITSM Practice," hosted by Luigi Ferri, we delve into how DevSecOps, combined with ITIL® 4, enhances security in IT services. We explore the benefits and challenges from a customer's perspective, discuss proactive security practices, and offer practical tips for integrating DevSecOps effectively. This integration is crucial for managing modern cybersecurity threats and ensuring rapid recovery from disruptions.
In this episode, we answer to:
How does DevSecOps change the security landscape in IT services?
What are the pros and cons of DevSecOps from a customer's p...
2024-10-0808 min
Defense Unicorns, A PodcastConnecting DevSecOps to Boyd’s Theories with Mark McGrathIn this episode of the Defense Unicorns Podcast, Rebecca sits down with Mark McGrath, a Marine Corps veteran turned asset manager and consultant, to explore how modern DevSecOps practices intersect with John Boyd's theories. Mark’s deep understanding of Boyd's OODA loop—observe, orient, decide, act—shapes how he helps clients in industries like manufacturing, energy, and public relations respond to complexity and streamline decision-making, much like DevSecOps optimizes software development and deployment.Diving into the legacy of John Boyd and going beyond the OODA loop, Mark discusses Boyd’s influence on business strategy, finance, and software developm...
2024-09-1952 min
Hear Remarkable Narration Elevate Every Scene Into Unforgettable Emotional Storytelling Experiences InstantlyLearning DevSecOps Audiobook by Steve SuehringListen to full audiobook for free :https://audiobookzap.com/freeTitle: Learning DevSecOpsSubtitle: A Practical Guide to Processes and ToolsCategories: Computer, Computer Science, Security, Software Development, TechnologyAuthor: Steve SuehringNarrator: Chris SorensenPublisher: Ascent AudioRelease date: 08-27-2024Language: EnglishSummary:How do some organizations maintain 24-7 internet-scale operations? How can organizations integrate security while deploying new features? How do organizations increase security within their DevOps processes? This practical guide helps you answer those questions. Steve Suehring provides unique content to help practitioners...
2024-08-2700 min
Bezpieczny Kod PodcastDevSecOps - Od Czego Zacząć. O Mentoringu i Dashboardach - Bezpieczny Kod x Katarzyna BrzozowskaNowy odcinek podcastu z Katarzyną Brzozowską - doświadczoną specjalistką DevSecOps!
Kasia dzieli się swoją inspirującą ścieżką kariery - od przebranżowienia się do IT, poprzez rolę administratora Linuxa, SysOps i DevOps, aż po obecne stanowisko DevSecOps Engineer.
Kluczowe tematy:
* Jak rozpocząć karierę w IT - wartość darmowych warsztatów i samodzielnej nauki
* Narzędzia w pracy DevSecOps: SonarQube, Snyk, Trivy
* Budowanie wartościowych dashboardów bezpieczeństwa
* Doświadczenia z mentoringu dla początkujących w IT
* Platformy do nauki cyberb...
2024-08-1936 min
InfosecTrainHow to Become a DevSecOps Engineer in 2024?What is DevSecOps?
DevSecOps builds upon DevOps, which combines software development with IT operations to enhance application deployment speed and competitiveness. DevOps has become standard practice in application development, facilitated by IT advancements like cloud computing.
DevSecOps, an extension of DevOps, integrates security practices into every DevOps phase. It fosters a ‘Security as Code’ culture through continuous collaboration between Release Engineers and Security teams.
What is a DevSecOps Engineer?
DevSecOps Engineers play a crucial role in configuring IT infrastructure, proactively identifying security vulnerabilities, and ensuring the security of the software development proc...
2024-06-2405 min
InfosecTrainIntroduction to DevSecOps Maturity ModelDevSecOps is critical in today’s fast-paced software development landscape, emphasizing security integration to mitigate vulnerabilities and breaches. This methodology offers a structured approach, guiding organizations to enhance security within DevOps processes. The DevSecOps maturity model is a roadmap for progressing through its stages to strengthen security posture, accelerate software delivery, and foster collaboration. It signifies a significant change in the way security is addressed in today’s digital era, emerging as a crucial resource for managing the intricate challenges of modern software as organizations adopt DevSecOps practices. Its adoption is no longer optional but essential for staying ahead in tod...
2024-06-2105 min
InfosecTrainIs a DevSecOps Career Right for You in 2024?In the increasingly digital world, DevSecOps has emerged as a crucial career path for those seeking to contribute to the security landscape. By incorporating security practices into the software development process, DevSecOps professionals play a vital role in safeguarding organizations against cyber threats.
As we step into 2024, the demand for skilled DevSecOps professionals is only expected to grow. For example, according to a recent report by Glassdoor, the job outlook for DevSecOps engineers is projected to grow 37% from 2020 to 2030, much faster than the average for all occupations. This growth is being driven by the increasing adoption of...
2024-06-2004 min
Talking Security: Insights from Microsoft Security Experts#36 - DevSecOps Series - Mastering the Monitor Phase for Robust SecurityIn this insightful episode of the Talking Security podcast, we turn our focus to the Monitor phase of the DevSecOps cycle. Hosts Sander ten Brinke, Pouyan Khabazi, and Frans Oudendorp guide you through the intricacies of continuous monitoring, providing an in-depth analysis of how to effectively observe and respond to threats in real-time.This episode of our DevSecOps series will cover:An overview of the Monitor phase in DevSecOpsStrategies for setting up robust monitoring systemsTechniques for real-time threat detection and responseBalancing proactive and reactive security measuresJoin us as we dissect the tools and practices...
2024-06-1742 minTalking Security: Insights from Microsoft Security Experts#35 - DevSecOps Series – How to release Software Securely in a DevSecOps Pipeline?In this episode of the Talking Security podcast, we delve into the essentials of release code securely within a DevSecOps pipeline. Join hosts Sander ten Brinke, Pouyan Khabazi, and Frans Oudendorp as they explore key strategies and best practices for integrating security into every stage of software development and deployment.As part of our DevSecOps series, this episode covers:- The fundamentals of DevSecOps- Critical security measures for code release- Tips for maintaining security without compromising speed or efficiencyWhether you're a seasoned professional or new to...
2024-05-2734 min
TechTalks the Podcast by ipt#23 Navigieren durch DevSecOps & Platform Engineering – Herausforderungen & StrategienIn dieser Podcast-Episode tauchen IT Architect Florian Stelzer und Senior Consultant Sergen Sentürk tief in die (sichere) Welt von Applikationen und Plattformen ein und beleuchten die Herausforderungen, denen Applikations- und Plattformentwickler und -entwicklerinnen derzeit gegenüberstehen. Das Themengebiet nennt sich DevSecOps. Dabei werfen sie einen Blick darauf, wie diese Herausforderungen die Team- und Projektarbeit beeinflussen. Und sie stellen sich der Frage: Was passiert, wenn DevSecOps nicht wie erwartet funktioniert und welche Schritte können unternommen werden, um dennoch erfolgreich zu sein?Diese Fragen werden beantwortet:(02:01) Welche aktuellen Herausforderungen beeinflussen App- und Plattformentwickler, sowie dere...
2024-05-1216 min
Cyber Sentries: AI Insight to Cloud SecurityAI Revolution in DevSecOps: Insights from John BushUnlocking the Power of AI in DevSecOpsIn this episode of Cyber Sentries, host John Richards sits down with John Bush, solutions architect at GitLab, to explore how artificial intelligence is transforming the day-to-day lives of developers. Bush, who has been coding since childhood, shares his insights on how AI is becoming embedded into every aspect of the DevSecOps pipeline, from writing code to identifying and remediating security vulnerabilities.John and Bush dive deep into GitLab's AI-powered features, collectively known as Duo, which are sprinkled throughout the software development process. They discuss how these features...
2024-05-0833 minTalking Security: Insights from Microsoft Security Experts#34 - DevSecOps Series – Demystifying the Test ProcessWelcome to the latest episode of the TalkingSecurity podcast, where we delve into the world of DevSecOps. In this episode, “Demystifying the Test Process,” we unpack the essentials of testing and its significance in the DevSecOps pipeline.🔍 What’s Inside:- Automated Testing: Discover the transformative power of automation in testing.- Security Integration: Learn how to weave security seamlessly into your test processes.- Expert Advice: Hear from industry veterans about navigating the challenges of DevSecOps testing.🎧 Listen and Learn: Whether you’re a DevSecOps newbie or a seasoned pract...
2024-05-0633 min
DSO OverflowS4Ep4 - IoT, AI and DevSecOps with Darren RichardsonDSO Overflow S4EP4IoT, AI and DevSecOpswithDarren RichardsonIn this month's episode, Jess and Glenn speak with networking graduate, security enthusiast, coder and giant with a great bushy beard Darren Richardson from Eficode.Darren is an IT graduate specializing in system administration, network operation and information security with experience in Cisco IOS operation and network management. He has a passion for information security with a bias towards offensive security and ethical hacking.In this episode, Darren talks about the inherent security challenges of using...
2024-04-0934 min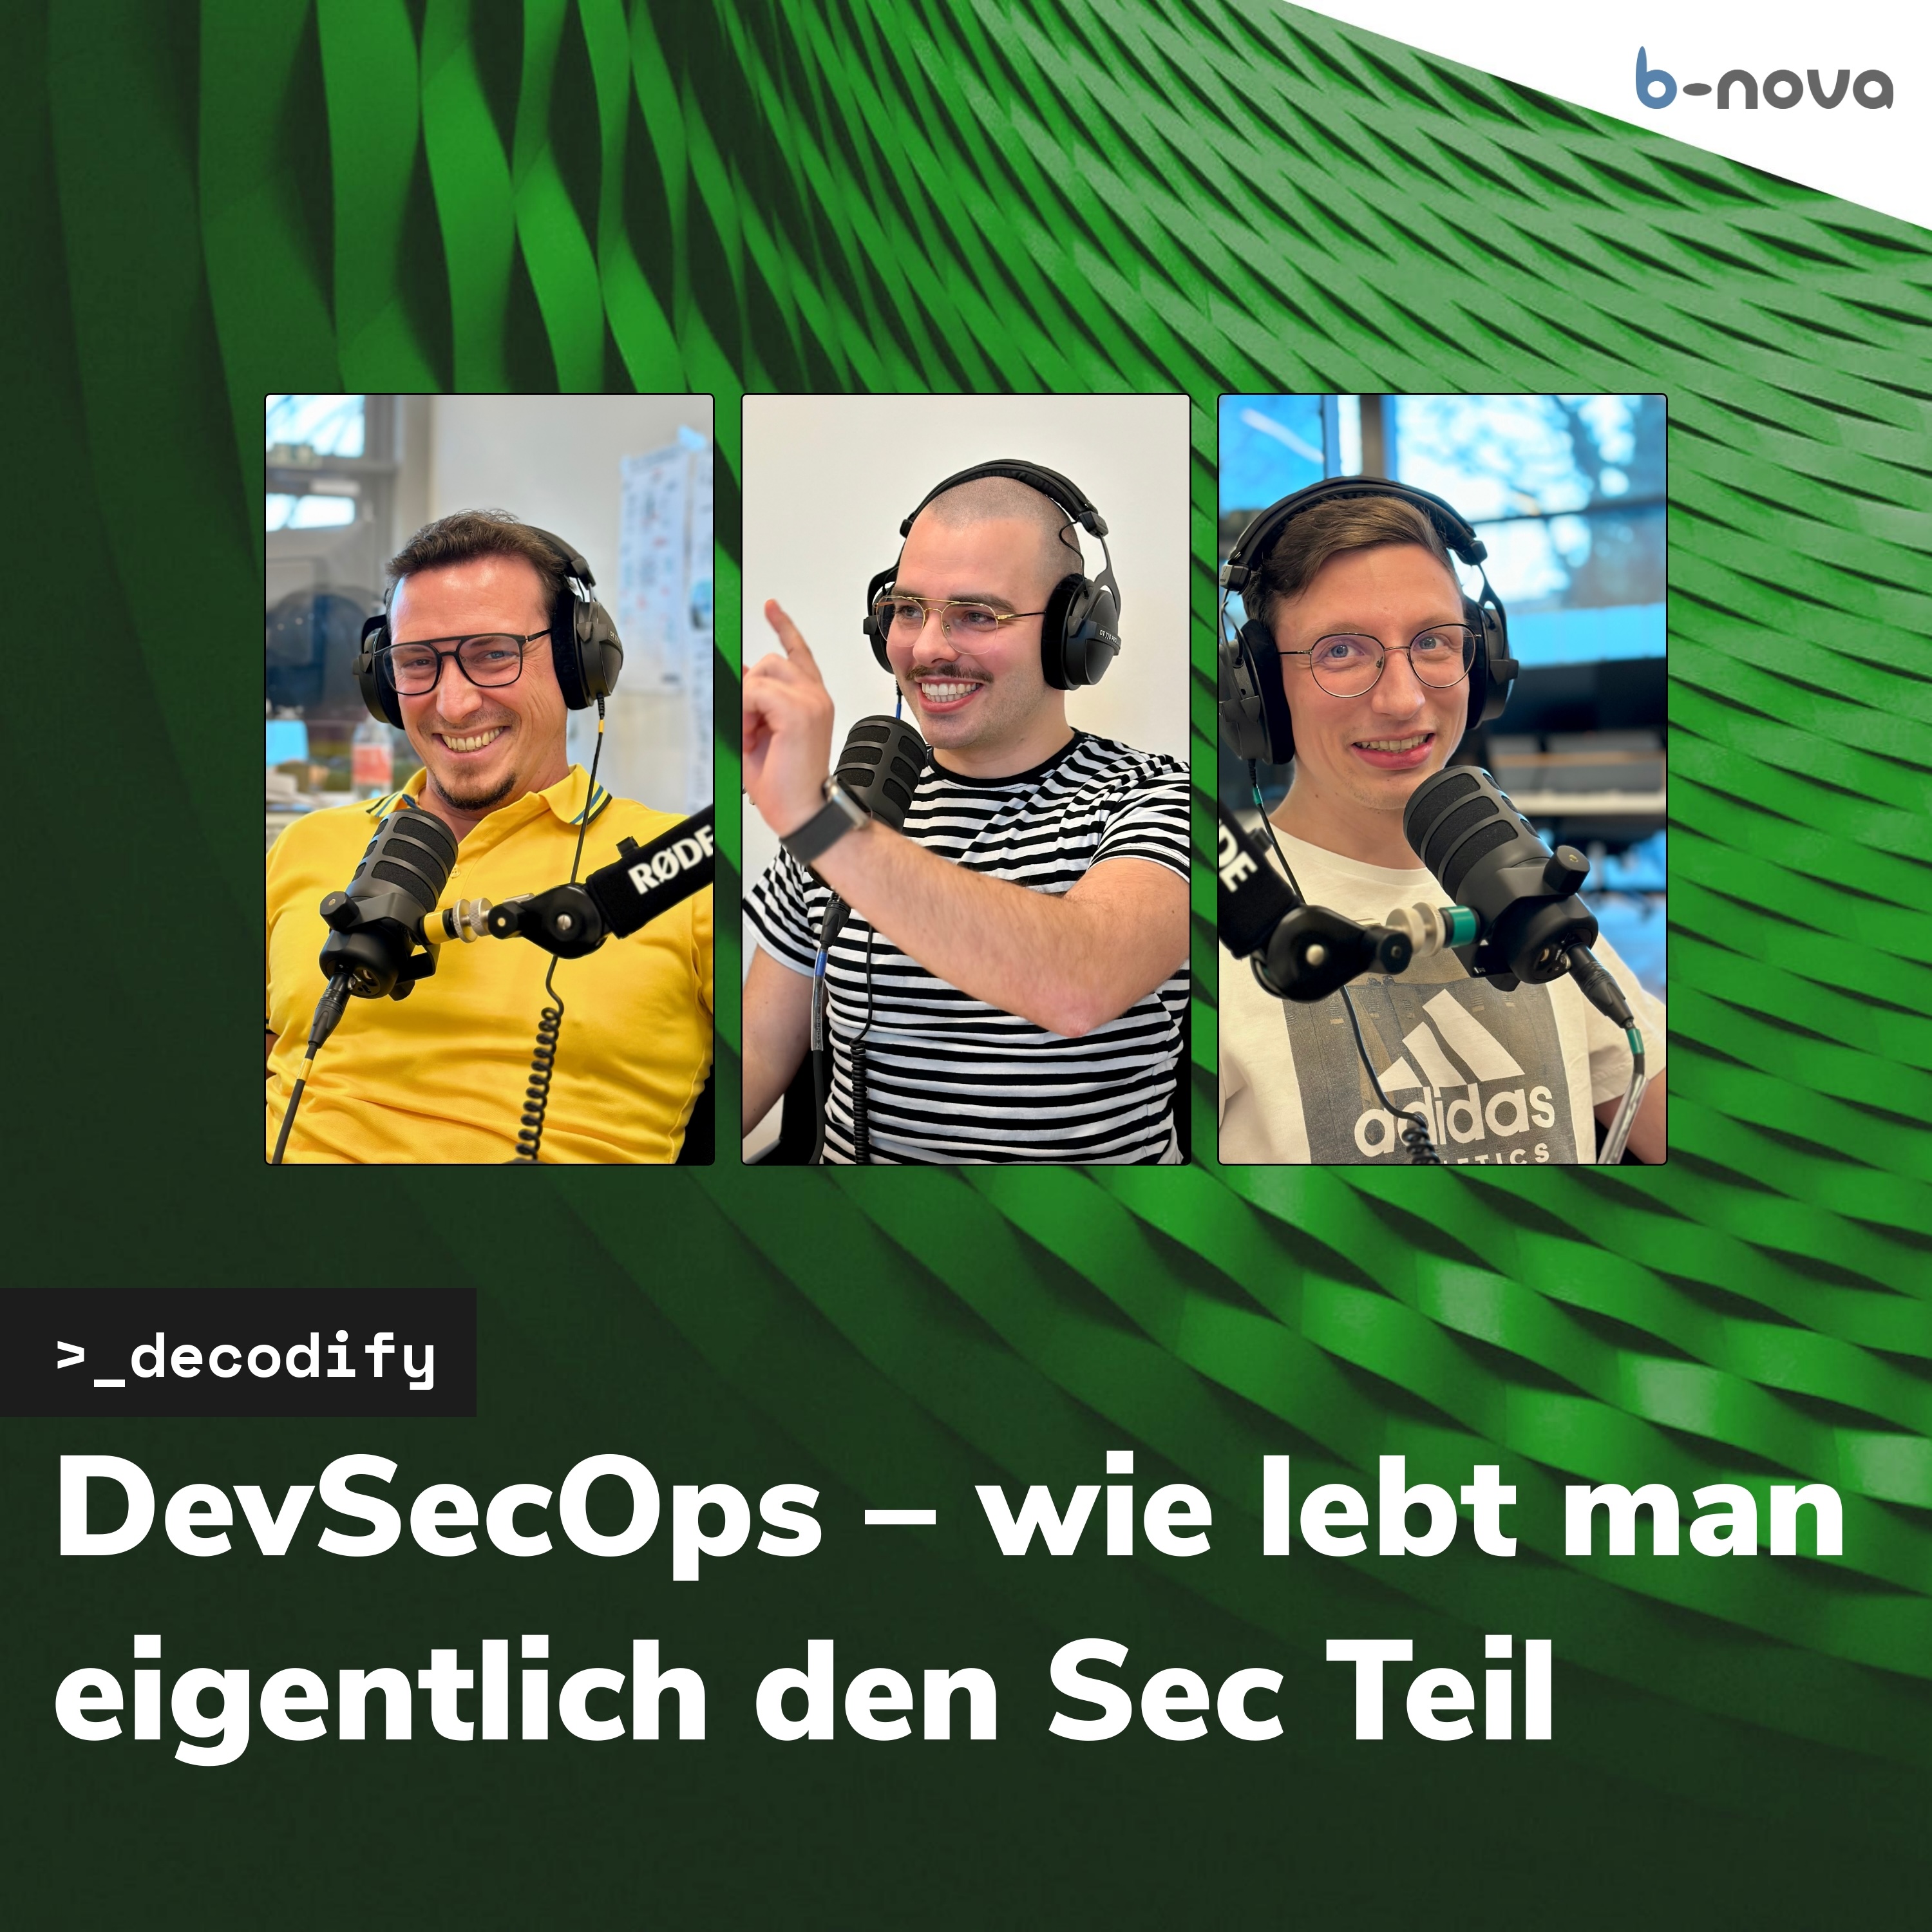
decodifyDevSecOps – wie lebt man eigentlich den Sec TeilDer Sec Teil in DevSecOps, nur ein Alibi oder eine Notwendigkeit? Wie lebt man den Security-Aspekt von DevOps, was heisst das praktisch für einen Entwickler oder eine IT-Abteilung?In dieser Folge von decodify widmen wir, Stefan, Ricky und Tom, uns dem spannenden Thema DevSecOps. Nach einen kurzen Recap zum Thema DevOps erörtern wir, was DevSecOps genau bedeutet und wie es sich von traditionellem DevOps und der klassischen Softwareentwicklung abhebt.Dabei beleuchten wir die zentrale Bedeutung der Sicherheit im Entwicklungsprozess, sprechen über die Schlüsselprinzipien, die für eine erfolgreiche Integration von Sicherheitsmaßnahmen notwendig sind, u...
2024-04-0345 min
The DevSecOps Talks PodcastDEVSECOPS Talks #62 - The DevSecOps Perspective: Key Takeaways From Re:Invent 2023In this episode of DevSecOps Talks, Andrey and Mattias discuss the latest announcements from re:Invent 2023 that are most relevant to DevSecOps practitioners. Which announcements are worth paying attention to? What are the implications for the DevSecOps community? Join us as we dive into the latest developments from AWS.
Connect with us on LinkedIn or Twitter (see info at https://devsecops.fm/about/). We are happy to answer any questions, hear suggestions for new episodes, or hear from you, our listeners.
2024-03-0233 min
InfosecTrainIntroduction to DevSecOps | What is Software Development Lifecycle?In today's fast-paced tech world, understanding the intricacies of DevSecOps and the Software Development Lifecycle (SDLC) is crucial for anyone looking to excel in software development. This Podcast, "Introduction to DevSecOps" is your gateway to mastering these essential concepts. Throughout this session, we'll dive deep into the world of DevSecOps, exploring its significance in modern software development and how it integrates with the SDLC to enhance security, efficiency, and collaboration across development teams.
DevSecOps, a methodology that integrates security practices within the DevOps process, is rapidly becoming a necessity in software development. By listening to this Podcast, you'll understand...
2024-02-291h 10
InfosecTrain10 Skills DevSecOps Engineers Must Master in 2024As per the ReportLinker report, the DevSecOps market is anticipated to expand at a 27.7% CAGR between 2022 and 2030, with an estimated market size exceeding USD 40.6 billion by 2030. This surge is primarily driven by the growing emphasis on security in software development and IT operations
In the modern age of advanced technology, the need for DevSecOps Engineers is surging significantly. As businesses seek to expedite their development procedures without compromising stringent security measures, these experts bridge the gaps between software development, security protocols, and operational efficiency. This article aims to delve into the most essential skill sets for DevSecOps En...
2024-01-1505 min
Scaling Tech - The Blueprint for Successful Tech TeamsThe DevSecOps Playbook: Deliver Continuous Security at Speed with Sean D. MackWhat is DevSecOps, and how can we embrace it as we continue improving our systems development cycle?To answer this important question is Sean D. Mack, a transformational technology leader who has literally written the book, ‘The DevSecOps Playbook: Deliver Continuous Security at Speed’.Appreciating the crucial role that security (at speed!) plays in your DevOps process begins with understanding company culture. It’s not so much about understanding the tools (“moving to the cloud”) as it is about the People, Process, and Technology. All the sta...
2023-12-1929 min
Q & A Series with Suresh GPWhat is the Future of DevSecOps in a Recession? | Q & A series with Suresh GP | Episode 50In this 50th episode of the DevSecOps Q&A series, Suresh GP shares his insights on what the future of DevSecOps looks like in a recession. Suresh discusses the various trends that have been appearing in DevSecOps over the past few years and how they will continue to develop in the next few years. He also shares some of the challenges that organizations are facing currently with DevSecOps, and what can be done to overcome them.If you're interested in learning more about the future of DevSecOps in a recession, then this is a Q&A series...
2023-12-1405 minQ & A Series with Suresh GPChallenges in implementing DevSecOps - Part 2 | Cyber Security | QnA Series with Suresh GP | Ep 41Challenges in implementing DevSecOps - Part 2 In this episode of the QnA Series with Suresh GP, we continue to discuss Challenges in implementing DevSecOps. In this episode, we discuss four more challenges that we’ve come across in our journey to implement DevSecOps.If you're new to DevSecOps or are struggling with any of the challenges, this series is for you! In this series, we discuss common challenges and how to overcome them. So if you're looking for solutions to your DevSecOps challenges, keep tuned for more episodes!Here are some of the cha...
2023-12-1405 minQ & A Series with Suresh GPWhat is DevSecOps Practitioner Certification | QnA Series with Suresh GP | Episode 33How to get DevSecOps Practitioner Certification? In this episode of the QnA series, Suresh GP is going to cover 1. What is DevSecOps Practitioner?2. How to get DevSecOps Practitioner Certified?3. Agenda for the DevSecOps Practitioner Training?4. How to enroll for the upcoming DevSecOps Practitioner Training with TaUB Solutions?
2023-12-1405 min
Connect to Complete Audiobooks in High QualityThe DevSecOps Playbook: Deliver Continuous Security at Speed - Sean D. MackPlease visit https://thebookvoice.com/podcasts/1/audiobook/714159 to listen full audiobooks.
Title: The DevSecOps Playbook: Deliver Continuous Security at Speed
Author: Sean D. Mack
Narrator: William Sarris
Format: Unabridged Audiobook
Length: 7 hours 9 minutes
Release date: November 21, 2023
Genres: Computers & Technology
Publisher's Summary: An essential and up-to-date guide to DevSecOps In The DevSecOps Playbook: Deliver Continuous Security at Speed, the chief information and information security officer at Wiley, Sean D. Mack, delivers an insightful and practical discussion of how to keep your business secure. You'll learn how to leverage the classic triad of people, process...
2023-11-217h 09
InfosecTrainWhy choose the DevSecOps Engineer course from InfosecTrain?What is DevSecOps?
DevSecOps, short for Development, Security, and Operations, is an approach to software development that integrates security practices into the entire Software Development Life Cycle (SDLC). It extends the principles of DevOps, which emphasizes collaboration and integration between development and IT operations teams, to include security considerations from the very beginning of the development process.
The DevSecOps Engineer’s objective is to make security an essential part of the development process rather than an afterthought or a distinct step. Organizations can establish a more proactive and simplified approach to discovering and addressing security vu...
2023-09-1505 min
InfosecTrainWhy Choose DevSecOps Practical Course with InfosecTrain?What is DevSecOps?
A technique to software development known as DevSecOps, or Development, Security, and Operations, incorporates security practices across the whole Software Development Lifecycle (SDLC). It extends the principles of DevOps, which emphasizes collaboration and integration between development and IT operations teams, to include security considerations from the beginning of the development process.
What is the DevSecOps Practical Course with InfosecTrain?
The DevSecOps Practical training course from InfosecTrain offers participants an all-encompassing, hands-on learning experience, equipping them with the practical expertise needed to implement DevSecOps practices within the context of...
2023-09-1205 min
SilverLining ILSilverLining Episode 59: Understanding the six pillars of DevSecopsGuest: Sam Sehgal, Co-Chair for the CSA DevSecOps working group and program Lead - DevSecOps Strategy and Architecture, Dell
Language: English
Abstract
DevSecOps, the integration of security practices into the DevOps methodology, has become a prominent topic in the field of information security in recent years. This approach emphasizes the collaboration between development, operations, and security teams throughout the software development lifecycle.
In this episode, we had the opportunity to speak with Sam Sehgal, co-chair for the DevSecOps Working Group (WG) at the Cloud Security Alliance (CSA). Sam shed li...
2023-05-3032 min
DevSecOps Podcast#15 - Appsec, DevSecOps e Nuvem?Neste episódio especial, mergulhamos no emocionante mundo da segurança de aplicações e como ela se relaciona com a cultura DevSecOps. Vamos explorar as melhores práticas para garantir a segurança em todas as etapas SDL e como os profissionais de segurança podem trabalhar em colaboração com as equipes de desenvolvimento e operações. Batemos um papo com o especialista em segurança de aplicações, Magno Logan, que compartilha insights valiosos sobre os desafios comuns enfrentados pelas organizações quando se trata de garantir a segurança de seus aplicativos. Ele discute a importância de uma aborda...
2023-05-2450 min
Cloud Security PodcastWhat is DevSecOps? DevSecOps with Cloud & AI explained for 2023Cloud Security Podcast - What is DevSecOps in 2023 especially in a world of Cloud and AI which is top of mind for both application security, developers, cybersecurity professionals. In this episode we will share how the updated definition of DevSecOps in 2023 has been redefined with Cloud and AI, also how does one measure success for DevSecOps.
Episode ShowNotes, Links and Transcript on Cloud Security Podcast: www.cloudsecuritypodcast.tv
FREE CLOUD BOOTCAMPs on www.cloudsecuritybootcamp.com
Host Twitter: Ashish Rajan (@hashishrajan)
Podcast Twitter - @CloudSecPod @CloudSecureNews
If you want to watch videos of...
2023-05-2314 min
Cognixia PodcastReshaping Developer Roles in DevSecOps with AIOne such area where artificial intelligence is making quite a mark is DevSecOps. We are going to take a quick minute here to tell everybody what is DevSecOps. DevSecOps is the practice of integrating security testing at every stage of the software development process. This would include the tools & processes which facilitate collaboration among developers, security specialists, operations team members, etc. to ensure that the final product, the software, or the application is both efficient and secure. To put it in a very simplified form, DevSecOps adds the element of security to the DevOps culture, weaving it into the...
2023-05-0610 min
Security StreamАнтон Гаврилов - Что такое DevSecOps и зачем он нужен?Что такое DevSecOps и зачем он нужен?Откуда берутся DevSecOps-специалисты и что они должны уметь?Обсуждаем эти и другие вопросы с нашим гостем.В новом выпуске второго сезона – Антон Гаврилов, BDM по направлению DevSecOps в компании «Инфосистемы Джет».Автор и ведущий подкаста – менеджер по развитию UserGate Иван Чернов.Краткое содержание беседы:– Чем отличается DevOps от DevSecOps;– Кому нужен DevSecOps;– Где учиться начинающим AppSec и DevSecOps-специалистам и нужно ли уметь программировать;– Чему может научиться начинающий ИБшник у линуксового админа.
2023-04-1050 min
The Virtual CISO PodcastEp 114: 4 Tactical Steps To Implementing DevSecOps In 2023DevSecOps is the practice of integrating security testing at every stage of the software development process. With DevSecOps, training and educating all teams in risk, security, and mitigation at all stages of development is a top priority– traditionally, app developers don't pay much attention to security, which increases the risk of vulnerable code being deployed and the application being compromised. To learn more about DevSecOps in this episode, your host John Verry, sits down with André Keartland, Solutions Architect with Netsurit Professional Services, to discuss tactical steps to implement DevSecOps in 2023.In this episode, Join us as...
2023-03-2851 minCloud Security PodcastIS THERE DEVSECOPS IN CLOUD? 🤔Cloud Security Podcast - This month we are talking about "Cloud Security - the Leadership View" and for the final episode in this series, we spoke to Guy Podjarny ( GuyPo's Linkedin). If you are working on building or securing Cloud resources, can you truly imagine solving the next log4j or AWS/Azure/GCP vulnerability without including the help of Platform Engineers or IT engineers? This is the bigger picture of what we CyberSecurity people have to do day in day out. We work with wider team members
Episode ShowNotes, Links and Transcript on Cloud Security Podcast: www...
2023-03-2850 min
Software Engineering Institute (SEI) Webcast SeriesDoes your DevSecOps Pipeline only Function as Intended?Understanding and articulating cybersecurity risk is hard. With the adoption of DevSecOps tools and techniques and the increased coupling between the product being built and the tools used to build them, the attack surface of the product continues to grow by incorporating segments of the development environment. Thus, many enterprises are concerned that DevSecOps pipeline weaknesses can be abused to inject exploitable vulnerabilities into their products and services. Using Model Based Systems Engineering (MBSE), a DevSecOps model can be built that considers system assurance and enables organizations to design and execute a fully integrated DevSecOps strategy in...
2023-01-1352 min
Post Mortem#19 Le DevSecOps à l'US Air ForceLe Department of Defense américain, c’est plus de 2.9 millions de personnels dont plus de 320 000 personnels à l’U.S. Air Force.
Déployer et maintenir du logiciel opérationnel à cette échelle - dans un contexte de compétition international grandissante - nécessite de pouvoir ajuster rapidement ses priorités, de prototyper et déployer des solutions sous courtes échéances.
Bref, de pouvoir pousser en production en quelques heures (voir minutes) et non plus en mois, cela avec des contraintes fortes en cybersécurité.
Nicolas Chaillan fut le...
2022-06-0530 min
Café Debug seu podcast de tecnologia#93 O que é DevSecOps?Fizemos um bate papo sobre DevSecOps, que significa desenvolvimento segurança e operações. Ou seja, é pensar na segurança da aplicação e da infraestrutura desde o ínicio. Talvez seja um tema novo para você ou não, equipes devem automatizar a segurança para proteger seu ambiente e os dados. Assuntos abordados no tema O que é DevSecOps? Sobre abordagens DevSecOps: Shift-left Descentralizar a segurança: difundir segurança em outros times Técnicas de segurança e seu uso durante o processo CI/CD Como funciona o processo de automatização da segurança do DevSecOps? Fator...
2022-03-2153 min
DevOps State of MindWhat do DevSecOps and Formula 1 have in common?Episode Summary: Is DevSecOps the answer to effective cloud migration? In this episode Liesse will talk to Josh Minthorne, Co-founder and Global Technology Director of Axcelinno. Axcelinno is an IT Technology Consultancy and Professional Services company that helps organizations define and implement their DevSecOps adoption and cloud migration. Liesse and Josh will talk about why the security landscape has made companies hesitant to move to the cloud and what they can do to migrate with confidence. About: Josh Minthorne, Co-founder and Global Technology Director of AxcelinnoJosh combines his passion for technology and innovation to h...
2022-02-1532 min
The Somerford PodcastWhat is DevSecOps and why do we need it?—Splunk Observability explained: Ft. Splunk DevOps AdvocateAnne is once again joined by Chris Riley, Technology Advocate at Splunk, for a conversation about DevSecOps. They explore "What is DevSecOps and why do we need it?", alongside tangible examples and getting realistic with customer challenges and what next steps they should take.✓ Watch/Read Chris Riley's "Enabling DevSecOps and Securing the Software Factory With Splunk" .conf21 session:▶ https://www.somerfordassociates.com/devsecops-explained-splunk-observability-podcast-register/✓ Register for our 'Splunk4Rookies - Observability' Virtual Workshops: ▶ https://www.somerfordassociates.com/splunk-devops-virtual-workshop/━━━━▶ Listen on Spotify: https://open.spotify.com/show/00soJ9kAQuVCh9EBRHOGzJ▶ Listen on Goo...
2022-01-1438 min
Хабр ПодкастыХабр ПРО // Треугольник DevSecOps: как объединить инструменты, процессы и знания о безопасностиНастраивать и контролировать процессы в IT-компании не проще, чем пилить код. Преуспеть в этом помогает DevOps, естественным продолжением которого в сфере информационной безопасности стал DevSecOps. О нём и поговорим.
Вместе с нашими гостями мы рассмотрели Ивана-царевича как модель угрозы; обсудили, как быть на шаг впереди злоумышленников; как сложить слово «безопасность» из процессов, инструментов и знаний; какая главная цель DevSecOps, как перейти к нему от DevOps и с чего надо начиать внедрение и изучение этих практик.
Мы взглянули на вопрос с двух сторон: реализации на практике и разработки инструментов. В этом нам помогли Алексей Бабенко, лидер команды тестирования безопасности приложений (Мир Plat.Form) и Алексей Жуков, руководитель направления по развитию продуктов обеспечения процесса безопасной разработки (Positive Technologies).
1:20 Объясняем концепцию DevSecOps на примере бессмертия Кощея
6:50 Безопасник — не враг: DevSecOps — глазами пользователя и производителей инструментов
13:50 «Ребята в худи – это мы сами». Не просто искать баги, а предотвращать их появление
18:20 DevSecOps – надстройка над DevOps или нечто большее
22:50 Как от DevOps прейти к DevSecOps, какие препятствия и сложности возникают
32:20 Определяем, соответствуют ли ваши процессы концепции безопасной разработки
32:20 Подходы, инструменты, люди – что важнее для DevSecOps (или зачем нужны отчёты на 100500 страниц)
38:40 Как безопаснику найти союзников среди разработчиков
42:30 С каких процессов начать переход к безопасному пайплайну разработки
51:20 Почему баги находят, но ничего с ними не делают (и как начать делать)
55:50 «Как стать DevSecOps и сделать это хорошо»: что почитать/посмотреть по теме
Прямой эфир прошёл 09 декабря. Запись доступна тут: https://youtu.be/rz_TjUmfY-Q
2021-12-101h 04
МимокрокодилВыпуск #12 - Денис Якимов. Про devsecops в большом банке и медийность с автором DevSecOps Wine канала.В этот раз у нас в гостях Денис Якимов занимающий позицию Head of DevSecOps в одном из крупнейших банков России, в широких кругах известен как автор нескольких популярных телеграмм каналов, таких как DevSecOps Wine CloudSec Wine и AppSec & DevSecOps Jobs.
Денис рассказал чем занимается человек на такой уникальной для СНГ позиции как Head of DevSecOps, что в ходит в круг его задач и поделится опытом их решения. Вторая часть подкаста освещает тему медийности в ИБ и её влияние на карьеру. Кажется, вышло интересно!
Внутри
- Как Денис пришел к текущей позиции
- Мнение Дениса о роли devsecops практик в ландшафте защиты компании
- Какие стоит покупать, а где лучший друг open source
- История развития DevSecOps wine канала
- Рассуждения не тему роли медийности в карьере ИБ специалиста
2021-12-0853 min
Effekten | digitalisering - kunskapDevSecOps – att utveckla säkert. Torbjörn Andersson (#170)Devops handlar om att föra samman systemutveckling och drift i iterativa loopar för att arbeta mer agilt. Lägg sedan till att det alltid finns hot mot systemet, som behöver hanteras, och vi får devsecops: Development Security Operations, ett sätt att integrera säkerhet i utvecklingsprocessen. Okej, det var många buzzwords i en mening… I detta avsnitt avdramatiserar vår säkerhetsexpert Torbjörn säkerhetsarbetet. Förr hade man ett säkerhetsteam; nu ska alla utvecklare ha säkerhetshatten på för att utveckla och leverera kontinuerligt på ett säkert sätt.
"Man ska alltid ha en s...
2021-11-2922 minThe Application Security PodcastTimo Pagel -- DevSecOps Maturity ModelTimo Pagel has been in the IT industry for over fifteen years. After a system administrator and web developer career, he advises customers as a DevSecOps consultant and trainer. His focus is on security test automation for software and infrastructure and assessment of complex applications in the cloud. In his spare time, he teaches “Web and Application Security” at various universities. Timo joins us to talk about the OWASP DevSecOps Maturity Model or DSOMM. We explore maturity models, this specific one, how you can use it, and how to get started. We hope you enjoy this conversation with... After a ca...
2021-10-2731 min
DSO OverflowEP15: DevSecOps PersonasIn this episode, Steve and Glenn speak with Ed Tucker and Gary Robinson about the differences between DevSecOps personas.DevSecOps Personas – what Developers, Security, and Operations think when it comes to people/tech/processes/culture when it comes to rolling out DevSecOps programs. Each of these teams have different drivers, ambitions, blockers, and challenges when it comes to a successful DevSecOps program. As Dale Carnegie said, ‘The only way to get anyone to do anything, is to make them want to do it’ - all the tech and process in the world isn’t going to make it successf...
2021-10-2553 min
SilverLining ILSilverLining Episode 42: How to mature devsecops operationsGuest: Hemi Gur-Ary
Guest Title: Co-Founder & CEO at VATA
Abstract:
Various organizations around the world are struggling to build & mature their devsecops operations. DSOM (Devsecops Maturity Model) is an OWASP project designed to help organizations plan and prioritize their devsecops strategies. In this episode, Hemi Gur-Ary, co-founder at VATA and senior devsecops consultant, shares his insights about DSOM and how organizations can use it for reshaping their devsecops practices.
2021-10-0619 min
Konia PodcastEpisódio #5 - Jornada DevSecOpsNeste episódio especial conversaremos sobre DevSecOps, seus pilares, sua cultura e principalmente experiencias práticas através de uma Jornada DevSecOps. Participe da conversa e compartilhe sua experiência conosco.Pauta: O que é DevSecOps? DevSecOps é uma evolução do DevOps? Pessoas, processos, ferramentas... Qual a relação destes pilares do processo de DevSecOps e o seu negócio? Quando falamos da adoção de um cultura DevSecOps, estamos falando de qual nível de abrangência, ou seja, qual ou quais partes do ciclo de desenvolvimento alcançamos? Quais os principais desafios para se adotar um processo de D...
2021-07-3053 min
АйТиБорода#119 - Кибербез как процесс разработки / Кто такие DevSecOps’еры / Денис КораблевСегодня мы узнаем, как принципы кибербезопасности внедряются в процесс разработки, помогают от атак хакеров, и помагают программистам делать действительно качественный код. В гостях Products Director компании Positive Technologies Денис Кораблёв.
В выпуске мы поговорили про технический опыт Дениса (а он у него ооочень богатый), про концепции из DevSecOps: SSDL, SCA, NVD, DAST, SAST, RASP и про внедрение подходов к написанию безопасного кода.
Так что, заваривайте чаинский/кофеинский и погнали, будет кайфово!😉
ДОП. МАТЕРИАЛЫ:
- Positive Technologies: https://www.ptsecurity.com
- Материалы и ссылки из выпуска: https://t.me/itbeard/605
- Видео-версия выпуска: https://youtu.be/pfyguvafIS8
- Стать спонсором канала: https://www.youtube.com/itbeard/join
НАВИГАЦИЯ:
0:00 - Начало
3:16 - Продажа газет
7:04 - Физмат лицей
15:36 - Университет
22:37 - Поездка в Канаду
26:30 - Законный перехват трафика
31:48 - Работа в банке с low latency
32:48 - Алготрейдинг
37:36 - Собеседование в Skype
42:10 - Уход из Skype
43:12 - Как попал в Positive Technologies
51:30 - Что такое DevSecOps
53:20 - Почему раработчики не думают об уязвимостях
59:20 - Про внедрение DevSecOps в команде
1:12:15 - Виртуальные патчи
1:12:51 - Что меняется в процессах команды при внедрении DevSecOps
1:14:35 - Кто отвечает за периметр
1:15:27 - Security Champios
1:23:29 - Инструменты DevSecOps: SSDL, SCA, NVD, DAST, SAST etc.
1:25:56 - Динамические сканеры
1:26:58 - Статические сканеры
1:32:40 - Runtime Application Self Protection - RASP
1:36:05 - Безобасность зависимостей
1:37:00 - Конференции и источники информации
1:38:40 - РАНДОМ: SPA, за что бить разрабов и художественная литература
1:53:00 - КОНКУРС
МОИ КОНТАКТЫ:
- Подпишись на этот YouTube канал :)
- Telegram: https://t.me/itbeard
- Instagram: https://instagram.com/itbeard
- Twitter: https://twitter.com/iamitbeard
- SoundCloud: https://soundcloud.com/itbeard
- Discord: https://discord.gg/it
- Сайт: https://itbeard.com
#айтиборода #ityoutubersru #devsecops
2021-04-211h 54
ATARC Federal IT NewscastFederal DevSecOps: Pushing ForwardDevSecOps within the Federal landscape has been a topic of growing priority, implementation, and necessity over the past several years. Join this webinar to hear from leaders in DevSecOps practices as they discuss the current status, modern projects, and drive forward of Federal DevSecOps platforms used to push IT modernization, operational efficiency, and cybersecurity. Listen as topic experts discuss the middle point of where DevSecOps, Zero Trust, and enterprise IT as a service (ITaaS) meet, and create effective, secure, modern, operational systems within the Federal IT ecosystem. Hear first-hand the current status, challenges, successes, and vision for the future...
2021-03-221h 03Software Engineering Institute (SEI) Webcast SeriesModeling DevSecOps to Reduce the Time-to-Deploy and Increase ResiliencyMany organizations struggle in applying DevSecOps practices and principles in a cybersecurity-constrained environment because programs lack a consistent basis for managing software intensive development, cybersecurity, and operations in a high-speed lifecycle. We will discuss how an authoritative reference, or Platform Independent Model (PIM), is needed to fully design and execute an integrated DevSecOps strategy in which all stakeholder needs are addressed, such as engineering security into all aspects of the DevSecOps pipeline to include both the pipeline and the deployed system. We will discuss how a PIM of a DevSecOps system can be used to 1) Specify the...
2021-03-1159 min
Tech 'n Savvy3' Put the Security in DevSecOps with Abdel Sy FaneApril and Emily interview Abdel Sy Fane, a security manager with over 10 years of experience. They discuss how Abdel got into tech, DevSecOps, personal cybersecurity tips, and more!00:00 Intro + How Abdel got into tech and DevSecOps10:29 What is CSNP?13:11 Personal Cybersecurity Tips20:39 DevSecOps Overview41:33 A Day in the life of a DevSecOps engineer49:09 CyberSecurity and DevSecOps career adviceResources Mentioned (not owned or created by us!)OWASP: https://owasp.org/Awesome DevSecOps: https://github.com/devsecops/awesome-devsecopsAwesome Ethical Hacking Resources: https://github.com/husnainfareed/Awesome-Ethical-Hacking-ResourcesA...
2021-02-231h 04
Meet The GurusHow DevSecOps Skills Distinguish You | Tim Chase | Paul Siegel | Meet The GurusIn this Meet the Gurus session, Tim Chase takes us on the DevSecOps journey and helps you to understand how it is a vital skill in every engineer's toolkit.
What will you learn?
The average DevSecOps Engineer salary (USA) is $140,000 per year or $71.79 per hour.
Entry-level positions start at $78,000 per year while most experienced workers make up to $205,000 per year.
DevSecOps isn't going away anytime soon as Cloud computing, data science, IoT and related technologies explode.
Education and training are vital skills to differentiate the DevSecOps engineer.
You can learn DevSecOps from master trainers.
About...
2021-02-1930 min
The OWASP Podcast SeriesThe Ops Side of DevSecOps w/ Damon EdwardsWhen Shannon Lietz and the team at DevSecOps.org published the DevSecOps Manifesto six years ago, security was uppermost in their minds. The manifesto starts with a call to arms…
“Through Security as Code, we have and will learn that there is simply a better way for security practitioners, like us, to operate and contribute value with less friction. We know we must adapt our ways quickly and foster innovation to ensure data security and privacy issues are not left behind because we were too slow to change.”
The effect of the DevSecOps movement was not understood by many, other than t...
2021-01-2924 min
Business & Technology Insights from CapgeminiDevSecOps- Agile security in a world of fast digitalIn today’s digitally enabled world, organisations are constantly evolving their products and services to maintain a competitive advantage with the customer. Cloud Computing and software development practices such as DevOps enable organisations to achieve high levels of agility, but often do so at the expense of security. Traditional Security practices are failing to evolve at the same rate, and this has resulted in a number of high-profile organisations fall foul to cyber-attacks. However, if done correct, DevSecOps offers a solution to this problem. Join two DevSecOps experts from Capgemini Invent and Secure Code Warrior, as they discuss what DevSecOps me...
2020-04-1731 min
BeerSecOpsEP05: With Michael Man, The Creator and Organizer of The DevSecOps London GatheringSteve Giguere of Aqua Security met Michael Man, the creator and organizer of the DevSecOps London Gathering Meetup, who just won the DevSecCon Security leadership award for OUTSTANDING DEVSECOPS COMMUNITY OF 2019. Listen to this podcast to learn about these London-based events, how it all started and where it's going.
Related Links:
DevSecOps London Gathering Meetup
https://www.meetup.com/DevSecOps-London-Gathering/
Follow Michael Man on Twitter
https://twitter.com/DevSecOps_LG
Follow Michael Man on LinkedIn
https://www.linkedin.com/in/michael-man-3851734
2019-11-2634 min
The ObjectSharp PodcastDevSecOps: Security Driven Development with Azure Security CenterIn this episode, we chat with Shane Castle, ObjectSharp's Cloud Practice Lead, and Ahmad Harb, Senior Cloud Consultant with ObjectSharp, about the changing role of security with cloud-native and serverless architectures. Shane and Ahmad help us unpack the "buzzword" of DevSecOps, think about the role of security in modern software development, introduce us to tooling in Azure Security Center, and give us practical advice and guidance on how to get started with security driven development right now.
Minutes
00:30 - Introduction to today’s show on Azure DevOps with guests Dave Lloyd and Martin Woodward
3:15- Shane Ca...
2019-09-0334 min
DevOps ChatDevSecOps @ RSA Conference with James Wickett and Shannon LietzThe RSA Conference is just a month away. Once again RSAC promises to be the place where the world gathers around security. With upwards of 50,000 people attending, it is big by anyone's standard.
If you haven't already registered, here is a code for $100 dollars off a full conference pass (all sessions), 1U9DEVOPSFD
or get a free expo pass, 1U9DEVOPSXP
DevSecOps will be center stage this year, literally. Shannon Lietz, the found of DevSecOps.org will be keynoting as well as leading a week long track on DevSecOps. Appearing with Shannon, is another leader of the DevSecOps community, James...
2019-02-0717 min
DevOps ChatThe DevSecOps Scene at RSA Conference 2019 w/ Shannon LietzThe RSA Conference is just a month away. Once again RSAC promises to be the place where the world gathers around security. With upwards of 50,000 people attending, it is big by anyone's standard.
If you haven't already registered, here is a code for $100 dollars off a full conference pass (all sessions), 1U9DEVOPSFD a free expo pass,
1U9DEVOPSXP
DevSecOps will be center stage this year, literally. Shannon Lietz, the found of DevSecOps.org will be keynoting as well as leading a week long track on DevSecOps. Shannon is our guest in this DevOps Chat.
Part 2 of this chat where...
2019-02-0518 min